Latest Cybersecurity News and Articles
Financial sector saw an 80% increase in interactive intrusions
08 August 2023
Cyberattack trends were analyzed in a recent report by CrowdStrike. The report revealed a massive increase in identity-based intrusions.
Tom Gorup hired as Edigo Vice President of Security Services
08 August 2023
Tom Gorup has been hired as the Vice President of Security Services at Edigo. Gorup has 15 years of experience in the cybersecurity industry.
Meet the Brains Behind the Malware-Friendly AI Chat Service ‘WormGPT’
08 August 2023
WormGPT, a private new chatbot service advertised as a way to use Artificial Intelligence (AI) to help write malicious software without all the pesky prohibitions on such activity enforced by ChatGPT and Google Bard, has started adding restrictions on how the service can be used. Faced with customers trying to use WormGPT to create ransomware and phishing scams, the 23-year-old Portuguese programmer who created the project now says his service is slowly morphing into “a more controlled environment.”
The large language models (LLMs) made by ChatGPT parent OpenAI or Google or Microsoft all have various safety measures designed to prevent people from abusing them for nefarious purposes — such as creating malware or hate speech. In contrast, WormGPT has promoted itself as a new LLM that was created specifically for cybercrime activities.
MPs fiddled with voter ID as electoral data security burned
08 August 2023
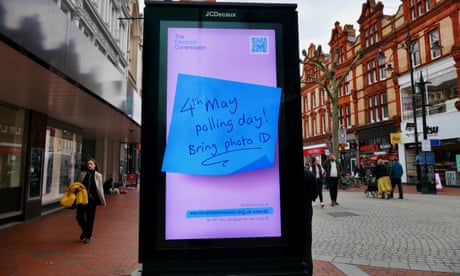 Electoral Commission hack is reminder of importance of protecting democratic system where it countsIt turns out that while Conservative ministers were spending hours of parliamentary time in 2021-22 introducing requirements for voters to produce ID at polling stations – to protect elections against a threat most experts believed was negligible – the Electoral Commission was being hacked by “hostile actors”.These hackers, who have not been identified and whose motivations are unclear, were able to access the data, such as home addresses, of millions of voters, many of whom choose not to make that information publicly available. Continue reading...
Ukrainian State Agencies Targeted with Open-Source Malware MerlinAgent
08 August 2023
In early August, an unidentified threat actor tracked as UAC-0154 sent malicious emails to its targets, purportedly containing security tips from Ukraine's computer emergency response team (CERT-UA).
Hackers Increasingly Abuse Cloudflare Tunnels for Stealthy Connections
08 August 2023
Cloudflare Tunnels provide a range of access controls, gateway configurations, team management, and user analytics, giving users a high degree of control over the tunnel and the exposed compromised services.
New Malware Campaign Targets Inexperienced Cybercriminals with OpenBullet Configs
08 August 2023
A new malware campaign has been observed making use of malicious OpenBullet configuration files to target inexperienced cybercriminals with the goal of delivering a remote access trojan (RAT) capable of stealing sensitive information.
New Threat Actor Targets Bulgaria, China, Vietnam, and Other Countries With Customized Yashma Ransomware
08 August 2023
The threat actor behind this operation uses an uncommon technique of downloading the ransom note from a GitHub repository, evading detection by embedding it in an embedded batch file.
Report: Two-Thirds of UK Sites Vulnerable to Bad Bots
08 August 2023
The majority (66%) of UK websites are unable to block simple bot attacks, exposing their businesses to fraud, account compromise, and much more, according to a report by DataDome.
QakBot Malware Operators Expand C2 Network with 15 New Servers
08 August 2023
The operators associated with the QakBot (aka QBot) malware have set up 15 new command-and-control (C2) servers as of late June 2023.
The findings are a continuation of the malware's infrastructure analysis from Team Cymru, and arrive a little over two months after Lumen Black Lotus Labs revealed that 25% of its C2 servers are only active for a single day.
"QakBot has a history of taking an
Invisible Ad Fraud Campaign Targets South Korean Android Users
08 August 2023
The discovery by McAfee’s Mobile Research Team shed light on a trend where certain apps distributed through Google Play discreetly load ads while the user’s device screen is turned off.
White House Pushes Cybersecurity Defense for K-12 Schools
08 August 2023
Typically understaffed and underfunded when it comes to cybersecurity, American K-12 schools have experienced a ramp-up in ransomware attacks, particularly after the pandemic forced the hasty adoption of remote tools for teaching.
HHS Warns Healthcare Sector of Attacks by Rhysida Ransomware Group
08 August 2023
Authorities are sounding the alarm about double-extortion attacks against healthcare and public health sector organizations by a relatively new ransomware-as-a-service group, Rhysida, which until recently had mainly focused on other industries.
CISA Unveils Cybersecurity Strategic Plan for Next Three Years
08 August 2023
The Cybersecurity Strategic Plan for fiscal years 2024-2026 outlines the agency’s plans for achieving a future where damaging cyberattacks are rare, organizations are resilient, and technology is secure by design.
Hackers Abusing Cloudflare Tunnels for Covert Communications
08 August 2023
New research has revealed that threat actors are abusing Cloudflare Tunnels to establish covert communication channels from compromised hosts and retain persistent access.
"Cloudflared is functionally very similar to ngrok," Nic Finn, a senior threat intelligence analyst at GuidePoint Security, said. "However, Cloudflared differs from ngrok in that it provides a lot more usability for free,
Massive Phishing Campaign Impersonates 340 Companies Using Over 800 Scam Domains
08 August 2023
The phishing operation, originating from Russia but pretending to be Ukrainian, utilized a high-quality single-page application to create convincing websites and steal credit card and bank details.
UK electoral registers hacked by ‘hostile actors’, elections watchdog reveals
08 August 2023
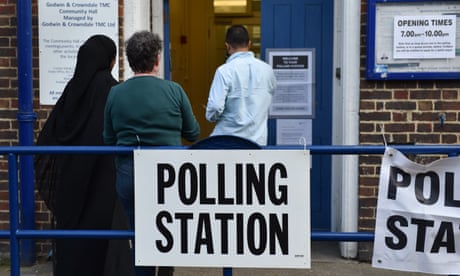 Elections watchdog says it is unable to say conclusively what information was accessed in cyber-attackThe UK’s elections watchdog has been targeted by a cyber-attack that enabled “hostile actors” to access electoral registers.The Electoral Commission revealed it had been hacked but was “not able to know conclusively” what information had been accessed and said it apologised to people whose information was accessible to the hackers. Continue reading...
Study: Higher education leaders see security as top priority
08 August 2023
A new study found that top institutional leaders are increasingly focused on improving both physical and network security.
UK: Over 200 Million Brits Have Data Compromised in Four Years
08 August 2023
Interestingly, the analysis also revealed that malicious attacks such as malware, phishing, and ransomware accounted for just a third (33%) of breaches reported to the ICO, versus 40% of incidents caused by insider threats.
CISA joins partners to warn of routinely exploited vulnerabilities
08 August 2023
A joint advisory urges organizations to implement secure by design practices and prioritize patching known exploited vulnerabilities to reduce risk of compromise.