Latest Cybersecurity News and Articles
CISA Warns Organizations of Exploited Vulnerability Affecting .NET, Visual Studio
11 August 2023
The vulnerability, tracked as CVE-2023-38180, was fixed by Microsoft with its August 2023 Patch Tuesday updates, which also address CVE-2023-36884, an Office vulnerability exploited by Russian threat actors.
Recent Ransomware Attacks Share Curiously Similar Tactics
11 August 2023
Over the course of three months beginning in January 2023, Sophos X-Ops investigated four different ransomware attacks, one involving Hive, two by Royal, and one by Black Basta, and noticed distinct similarities between the attacks.
Researchers Shed Light on APT31's Advanced Backdoors and Data Exfiltration Tactics
11 August 2023
The Chinese threat actor known as APT31 (aka Bronze Vinewood, Judgement Panda, or Violet Typhoon) has been linked to a set of advanced backdoors that are capable of exfiltrating harvested sensitive information to Dropbox.
The malware is part of a broader collection of more than 15 implants that have been put to use by the adversary in attacks targeting industrial organizations in Eastern Europe
Western Digital, Synology NAS Vulnerabilities Exposed Millions of Users’ Files
11 August 2023
Critical vulnerabilities discovered by IoT and industrial cybersecurity firm Claroty in Western Digital (WD) and Synology network-attached storage (NAS) products could have exposed the files of millions of users.
New SystemBC Malware Variant Targets South African Power Company
11 August 2023
An unknown threat actor has been linked to a cyber attack on a power generation company in South Africa with a new variant of the SystemBC malware called DroxiDat as a precursor to a suspected ransomware attack.
"The proxy-capable backdoor was deployed alongside Cobalt Strike Beacons in a South African nation's critical infrastructure," Kurt Baumgartner, principal security researcher at
EvilProxy Phishing Attack Surges in Last Five Months
11 August 2023
Proofpoint came across EvilProxy, a phishing platform, being used in a large-scale campaign targeting MFA-protected Microsoft 365 accounts, with over 120,000 phishing emails sent to more than hundreds of organizations. The campaign primarily targeted high-ranking executives. Organizations must enhance their email and web security to defend against advanced hybrid threats.
Why Cybersecurity is a Blue-Collar Job
11 August 2023
Alternative education options, such as vocational-technical schooling and industry-relevant certifications, offer cost-effective pathways for aspiring cybersecurity professionals.
Intel Addresses 80 Firmware, Software Vulnerabilities
11 August 2023
The most serious of the patched flaws, based on their CVSS score, are 18 high-severity issues allowing privilege escalation or, in a few cases, denial-of-service (DoS) attacks.
Lawsuits Mounting Against Florida Hospital in Wake of Breach
11 August 2023
Tampa General Hospital is facing at least three proposed federal class action lawsuits filed in recent days following the nonprofit Florida healthcare provider's disclosure late last month of a data theft incident that affected 1.3 million people.
Attackers Distribute Malware via Freeze.rs And SYK Crypter
11 August 2023
FortiGuard Labs has discovered a new injector written in the programming language Rust, which injects shellcode and introduces a malware called XWorm into a victim's system.
Symmetry Systems Raises $17.7M in Funding
11 August 2023
The $17.7 million insider funding round brings the total raised by the data security company to more than $35 million. ForgePoint Capital, Prefix Capital, W11 Capital Management, and TSG (The Syndicate Group) participated in the latest funding round.
SAP Patches Critical Vulnerability in PowerDesigner Product
11 August 2023
German software giant SAP has fixed more than a dozen new vulnerabilities with its August 2023 Patch Tuesday updates, including a critical flaw affecting the company’s PowerDesigner data modeling and enterprise architecture product.
Akamai Explores the Present Ransomware Scenario
11 August 2023
Ransomware groups are shifting their tactics from relying on phishing methods and are now prioritizing the exploitation of vulnerabilities to exfiltrate data from victims' systems. Additionally, these groups have adopted a more assertive strategy to extort and capitalize on vulnerabilities. They even invest in various avenues for financial profit, such as collaborating with other hackers to identify weaknesses in their ransomware code or leveraging Initial Access Brokers (IABs) to gain entry to their target victims.
15 New CODESYS SDK Flaws Expose OT Environments to Remote Attacks
11 August 2023
A set of 15 high-severity security flaws have been disclosed in the CODESYS V3 software development kit (SDK) that could result in remote code execution and denial-of-service under specific conditions, posing risks to operational technology (OT) environments.
The flaws, tracked from CVE-2022-47379 through CVE-2022-47393 and dubbed CoDe16, carry a CVSS score of 8.8 with the exception of
CISA Adds Microsoft .NET Vulnerability to KEV Catalog Due to Active Exploitation
10 August 2023
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a recently patched security flaw in Microsoft's .NET and Visual Studio products to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation.
Tracked as CVE-2023-38180 (CVSS score: 7.5), the high-severity flaw relates to a case denial-of-service (DoS) impacting .NET and Visual Studio.
It
77% of financial firms saw an increase in cyberattack frequency
10 August 2023
Cyberattacks against financial organizations were analyzed in a recent report, finding that 77% saw an increase in cyberattack frequency.
President Biden signs security technology executive order
10 August 2023
In an effort to protect sensitive technology, President Biden signed an executive order on regulating U.S. security technology investments.
The Guardian view on Northern Ireland’s data leak: putting lives at risk | Editorial
10 August 2023
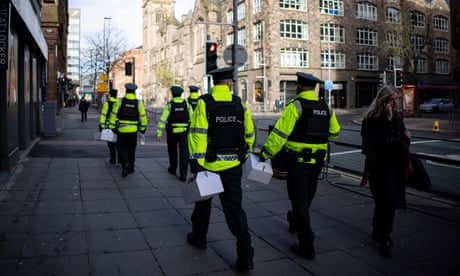 The police’s error is hard to forgive, but ministers must treat Northern Ireland’s wider human safety needs as a priority tooA new documentary film recounts a grim story from the Northern Ireland Troubles. Half a century ago, Thomas Niedermayer was a German businessman living in Belfast. At Christmas in 1973, he was kidnapped from his home by the IRA, possibly to be traded for imprisoned bombers, and murdered. His body was found in a shallow grave in 1980. Ten years on, his widow, Ingeborg, took her own life. A year after that, the Niedermayers’ younger daughter, Renate, killed herself. Another two years later, their elder daughter, Gabriella, did the same.The Niedermayer murder, as detailed in the Face Down documentary, was vicious. For the family, the damage lasted for generations, creating new victims and further tragedies. The lesson is frighteningly timely. This week, the Police Service of Northern Ireland mistakenly published an online spreadsheet detailing the surnames, initials, ranks or grades, locations and departments of all current PSNI officers and civilian staff members. The spreadsheet was not taken down for three hours. Approximately 10,000 people were listed. The consequences could endure for decades. Continue reading...
Sweet Security Raises $12M Seed Round for its Cloud Security Suite
10 August 2023
The $12 million seed round was led by Glilot Capital Partners, with participation from CyberArk Ventures and a number of angel investors including Gerhard Eschelbeck, a former CISO at Google, and Travis McPeak, who led product security at Databricks.
Encryption Flaws in Popular Chinese Language App Put Users' Typed Data at Risk
10 August 2023
The findings come from the University of Toronto's Citizen Lab, which carried out an analysis of the encryption mechanism used in Tencent's Sogou Input Method, an app that has over 455 million monthly active users across Windows, Android, and iOS.