Latest Cybersecurity News and Articles
Google Introduces First Quantum Resilient FIDO2 Security Key Implementation
17 August 2023
The development comes less than a week after the tech giant said it plans to add support for quantum-resistant encryption algorithms in Chrome 116 to set up symmetric keys in TLS connections.
If there is a lesson from the NI police data breach it is not to forget the cruelty of the Troubles | Martin Kettle
17 August 2023
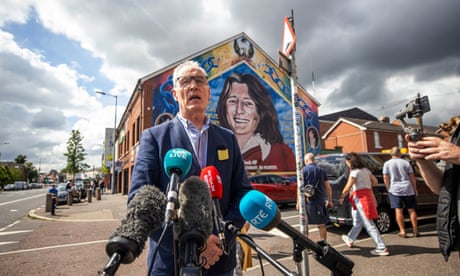 The leak could undermine security in Northern Ireland – restoring power sharing is a political necessity at this momentHalf of the people who live in these islands have no adult memory at all of the Northern Ireland troubles. Too many of those who can remember them have allowed the bombings, shootings, riots and violence to slip from their minds in the 25 years that have passed since a peace treaty was signed in 1998. But last week’s data leak by the Police Service of Northern Ireland (PSNI) ought to be a wake-up call for the forgetful, and a lightbulb moment for the unaware.Nine days ago, in response to a freedom of information request whose provenance remains unclear, someone in the PSNI mistakenly put the names, initials, ranks, place of work and departments of all of its 10,000 officers and staff online for about three hours before they were removed. Especially in a profession where police and their families were, and sometimes still are, regular targets, it was a spectacular security breach, even in these more peaceful times.Martin Kettle is a Guardian columnist Continue reading...
Unveiling the Sophisticated Statc Stealer
17 August 2023
Zscaler ThreatLabz detected and dissected Statc Stealer, a potent information-stealing malware targeting Windows systems. This C++-based malware effectively extracts sensitive data from popular web browsers, cryptocurrency wallets, and messaging apps like Telegram. To counteract the risks, the implementation of several proactive strategies such as education and awareness, robust antivirus solutions, and network monitoring, among others, is essential.
CISA Adds Citrix ShareFile Flaw to KEV Catalog Due to In-the-Wild Attacks
17 August 2023
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical security flaw in Citrix ShareFile storage zones controller to its Known Exploited Vulnerabilities (KEV) catalog, based on evidence of active in-the-wild exploitation.
Tracked as CVE-2023-24489 (CVSS score: 9.8), the shortcoming has been described as an improper access control bug that, if successfully exploited
70% of web applications have severe security gaps
16 August 2023
According to a CyCognito report, 74% of assets with personally identifiable information (PII) are vulnerable to at least one known major exploit.
Major U.S. Energy Organization Targeted in QR Code Phishing Attack
16 August 2023
According to Cofense, who spotted this campaign, this is the first time that QR codes have been used at this scale, indicating that more phishing actors may be testing their effectiveness as an attack vector.
Chrome 116 Patches 26 Vulnerabilities
16 August 2023
Google on Tuesday announced the release of Chrome 116 to the stable channel with patches for 26 vulnerabilities, including 21 reported by external researchers. Of the externally reported bugs, eight have a severity rating of ‘high.’
Report finds exposed sensitive data in more than 30% of cloud assets
16 August 2023
A new report reveals that more than 30% of cloud data assets contain sensitive information.
Experts Uncover Weaknesses in PowerShell Gallery Enabling Supply Chain Attacks
16 August 2023
The flaws have to do with the service's lax policy surrounding package names, lacking protections against typosquatting attacks, as a result enabling attackers to upload malicious PowerShell modules that appear genuine to unsuspecting users.
Chamber of Commerce Urges SEC to Delay Cyber Rule Implementation
16 August 2023
The U.S. Chamber of Commerce urged the Securities and Exchange Commission to delay by a year the effective date of new cybersecurity rules, saying the regulatory move could otherwise have “severe consequences” for companies.
Scott Sykes joins Asurity as Chief Information Security Officer
16 August 2023
Scott Sykes has been hired as CISO at Asurity Technologies. Sykes was previously CISO at Netcracker Technology and Tata Communications.
Raccoon Stealer Malware Returns With New Stealthier Version
16 August 2023
The developers of Raccoon Stealer information-stealing malware have ended their 6-month hiatus from hacker forums to promote a new 2.3.0 version of the malware to cybercriminals.
Automotive data privacy under scrutiny in California
16 August 2023
California regulators are examining how automakers and others handle data collected from internet-connected vehicles, the California Privacy Protection Agency said late last month.
Ransomware Attack on Rapattoni Disrupts US Real Estate Property Listings
16 August 2023
Real estate agents' ability to list or update property information has been compromised by an attack on California-based data services company Rapattoni, which hosts multiple listing services.
What's the State of Credential theft in 2023?
16 August 2023
At a little overt halfway through 2023, credential theft is still a major thorn in the side of IT teams. The heart of the problem is the value of data to cybercriminals and the evolution of the techniques they use to get hold of it. The 2023 Verizon Data Breach Investigations Report (DBIR) revealed that 83% of breaches involved external actors, with almost all attacks being financially motivated
Experts Uncover Weaknesses in PowerShell Gallery Enabling Supply Chain Attacks
16 August 2023
Active flaws in the PowerShell Gallery could be weaponized by threat actors to pull off supply chain attacks against the registry's users.
"These flaws make typosquatting attacks inevitable in this registry, while also making it extremely difficult for users to identify the true owner of a package," Aqua security researchers Mor Weinberger, Yakir Kadkoda, and Ilay Goldman said in a report shared
Clorox Cleans up Security Breach That Disrupted Operations
16 August 2023
The intrusion continues to disrupt "parts of the company's business operations," and it is "working diligently to respond to and address this issue, and is also coordinating with law enforcement," according to the Form 8-K submission.
Guide: How Google Workspace-based Organizations can leverage Chrome to improve Security
16 August 2023
More and more organizations are choosing Google Workspace as their default employee toolset of choice. But despite the productivity advantages, this organizational action also incurs a new security debt. Security teams now have to find a way to adjust their security architecture to this new cloud workload.
Some teams may rely on their existing network security solutions. According to a new guide
Prince George's County Public Schools Responds Suffers Network Outage Owing to Cyberattack
16 August 2023
District leaders initially said they were working to address a “broad network outage” that knocked out email and other services. On Monday night, the district released a statement saying 4,500 of the system’s 180,000 accounts were “impacted.”
Google Introduces First Quantum Resilient FIDO2 Security Key
16 August 2023
Google on Tuesday announced the first quantum resilient FIDO2 security key implementation as part of its OpenSK security keys initiative.
"This open-source hardware optimized implementation uses a novel ECC/Dilithium hybrid signature schema that benefits from the security of ECC against standard attacks and Dilithium's resilience against quantum attacks," Elie Bursztein and Fabian Kaczmarczyck