Latest Cybersecurity News and Articles
High-Profile CVEs Turn up in Vulnerability Exploit Sales
13 September 2023
Three reported purchases of vulnerability exploits on the dark web during the first half of the year included high-profile, actively exploited CVEs, according to research by Flashpoint.
Newly Discovered MetaStealer Malware Targets macOS Users
13 September 2023
A new MetaStealer malware has surfaced in the wild, targeting macOS business users. Written in Golang, the malware is distributed via social engineering tactics, where attackers pose as fake design clients and lure victims into executing malicious payloads. Apple’s XProtect update v2170 contains a detection signature for some versions of MetaStealer, for others, IOCs are to be utilized.
Ransomware: It Takes A Village, Says the UK NCSC
13 September 2023
Stopping the ransomware epidemic is less about tackling individual crypto-locking malware variants and more about combating the entire ecosystem of bad actors underpinning digital extortion, the British government said Monday.
Alert: New Kubernetes Vulnerabilities Enable Remote Attacks on Windows Endpoints
13 September 2023
Three interrelated high-severity security flaws discovered in Kubernetes could be exploited to achieve remote code execution with elevated privileges on Windows endpoints within a cluster.
The issues, tracked as CVE-2023-3676, CVE-2023-3893, and CVE-2023-3955, carry CVSS scores of 8.8 and impact all Kubernetes environments with Windows nodes. Fixes for the vulnerabilities were released on August
Nearly 15,000 Accounts Raided at Automaker Sites to Harvest Vehicle IDs
13 September 2023
Attackers appear to have deployed bots to break into customer accounts at several large automakers, then harvested important information about thousands of individual vehicles and offered it for sale in private Telegram channels, researchers said.
49% of survey respondents were fooled by ChatGPT
13 September 2023
A recent Beyond Identity survey analyzed how convincing generative artificial intelligence (AI) software ChatGPT was at tricking individuals.
CertifID, Which Develops Products To Prevent Wire Fraud, Raises $20M
13 September 2023
The real estate fraud prevention startup CertifID has raised $20 million in a funding round led by Arthur Ventures, bringing its valuation to over double its previous value.
Researchers Detail 8 Vulnerabilities in Azure HDInsight Analytics Service
13 September 2023
More details have emerged about a set of now-patched cross-site scripting (XSS) flaws in the Microsoft Azure HDInsight open-source analytics service that could be weaponized by a threat actor to carry out malicious activities.
"The identified vulnerabilities consisted of six stored XSS and two reflected XSS vulnerabilities, each of which could be exploited to perform unauthorized actions,
44% of IT leaders describe their organization as secure
13 September 2023
A report found that IT leaders believe cybersecurity concerns are negatively impacting their organization’s willingness to invest in innovative tech.
Stealthy Remcos Malware Attack Campaign Takes Aim at Colombian Firms
13 September 2023
The attackers employed highly obfuscated BAT files and multi-layered obfuscation techniques to evade detection and load the Remcos malware into memory, bypassing traditional antivirus and endpoint security solutions.
CoinEx Exchange Loses $27 Million Worth of Crypto in Suspected Hack
13 September 2023
A CoinEx hot wallet transferred $27 million of various tokens to a wallet with no previous history in what the exchange’s team has referred to as “anomalous withdrawals."
Microsoft Patches a Pair of Actively Exploited Zero-Days
13 September 2023
In total, Microsoft released 59 new patches addressing bugs across its product gamut. They affect Microsoft Windows, Exchange Server, Office, .NET and Visual Studio, Azure, Microsoft Dynamics, and Windows Defender.
Twitter chaos after Elon Musk takeover may have violated privacy order, DoJ alleges
13 September 2023
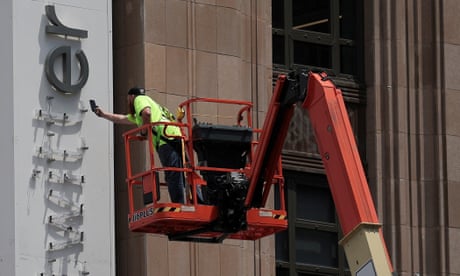 US Department of Justice questions compliance with FTC order on data security and privacy practicesElon Musk’s takeover of Twitter created a “chaotic environment” at the social media platform that may have violated a government order requiring an overhaul of its data security and privacy practices, according to a court filing.The US Department of Justice (DoJ) alleged in a legal filing on Tuesday that depositions from former employees at Twitter, now rebranded X, raised “serious questions” about whether the company was complying with an order imposed by the consumer and competition watchdog, the Federal Trade Commission (FTC). Continue reading...
Webinar: Identity Threat Detection & Response (ITDR) – Rips in Your Identity Fabric
13 September 2023
In today's digital age, SaaS applications have become the backbone of modern businesses. They streamline operations, enhance productivity, and foster innovation. But with great power comes great responsibility. As organizations integrate more SaaS applications into their workflows, they inadvertently open the door to a new era of security threats. The stakes? Your invaluable data and the trust
Redfly Group Compromised National Power Grid in Six-Months-Long Campaign
13 September 2023
The Redfly threat actor group used the ShadowPad Trojan to compromise a national grid in an Asian country, stealing credentials and maintaining a presence for up to six months.
Adobe Says Critical PDF Reader Zero-Day Being Exploited
13 September 2023
As part of its scheduled batch of Patch Tuesday updates, Adobe warned that hackers are exploiting a remotely exploitable vulnerability — CVE-2023-26369 — to launch code execution attacks.
Canadian Nurses Association Confirms Data Theft After Hackers Dump Stolen Information
13 September 2023
While operations were not affected, some systems were compromised. The ransomware groups Snatch and Nokoyawa claimed responsibility for the attack, with Snatch leaking 37 GB of data from the association.
Mozilla Rushes to Patch WebP Critical Zero-Day Exploit in Firefox and Thunderbird
13 September 2023
Mozilla on Tuesday released security updates to resolve a critical zero-day vulnerability in Firefox and Thunderbird that has been actively exploited in the wild, a day after Google released a fix for the issue in its Chrome browser.
Several Siemens ICS Products Impacted by Critical CodeMeter Vulnerability
13 September 2023
One of the advisories describes CVE-2023-3935, a critical vulnerability affecting Wibu Systems’ CodeMeter software licensing and protection technology, which is used by several Siemens products, including PSS, SIMATIC, SIMIT, SINEC, and SINEMA.
Rust-Written 3AM Ransomware: A Sneak Peek into a New Malware Family
13 September 2023
A new ransomware family called 3AM has emerged in the wild after it was detected in a single incident in which an unidentified affiliate deployed the strain following an unsuccessful attempt to deploy LockBit (aka Bitwise Spider or Syrphid) in the target network.
"3AM is written in Rust and appears to be a completely new malware family," the Symantec Threat Hunter Team, part of Broadcom, said in