Latest Cybersecurity News and Articles
APT42 Hackers Pose as Journalists to Harvest Credentials and Access Cloud Data
07 May 2024
The Iranian state-backed hacking outfit called APT42 is making use of enhanced social engineering schemes to infiltrate target networks and cloud environments.
Targets of the attack include Western and Middle Eastern NGOs, media organizations, academia, legal services and activists, Google Cloud subsidiary Mandiant said in a report published last week.
"APT42 was
Synopsys to Sell its Software Integrity Business to Clearlake Capital and Francisco Partners
07 May 2024
After the transaction, the business will operate independently as an application security testing software provider, with the current management team expected to lead the new entity.
China-Linked Hackers Used ROOTROT Webshell in MITRE Network Intrusion
07 May 2024
The MITRE Corporation has offered more details into the recently disclosed cyber attack, stating that the first evidence of the intrusion now dates back to December 31, 2023.
The attack, which came to light last month, singled out MITRE's Networked Experimentation, Research, and Virtualization Environment (NERVE) through the exploitation of two Ivanti Connect Secure zero-day
US Sets Sights on Partnerships to Counter Cyberthreats, Secure AI in New Global Cyber Strategy
07 May 2024
The new strategy of the U.S. government aims to defend against cyberattacks on critical infrastructure, prevent surveillance misuses, and promote digital solidarity among global partners.
Dangerous Scammers From the Yahoo Boys Group Operate Openly on Social Media
07 May 2024
The Yahoo Boys, a group of scammers primarily based in West Africa, openly operate on various social media platforms like Facebook, WhatsApp, and Telegram, engaging in fraudulent activities that range from romance fraud to business email compromise.
80% of data experts believe AI increases data security challenges
07 May 2024
A new report reveals that a majority of data experts agree that artificial intelligence is increasing data security challenges.
Krebs, Luber Added to Cyber Safety Review Board
07 May 2024
The Cyber Safety Review Board (CSRB) has added four new members, including Chris Krebs, former Director of the CISA, and David Luber, head of the NSA's Cybersecurity Directorate.
Ransomware Activity is Back on Track Despite Law Enforcement Efforts
07 May 2024
According to Corvus Insurance, ransomware activity surged in the first quarter of 2024, marking a 21% increase over the same period in 2023, despite disruptions to major ransomware groups like LockBit and ALPHV/BlackCat.
Global Fraud Prevention Leader BioCatch Valued at $1.3bn in Permira Takeover
07 May 2024
The acquisition will involve Permira buying out shares primarily from Bain Capital Tech Opportunities and Maverick Ventures, while existing shareholders Sapphire Ventures and Macquarie Capital will also increase their stakes in BioCatch.
Novel TunnelVision Attack Against Impacts Virtually All VPN Apps Through DHCP Server Manipulation
07 May 2024
The TunnelVision attack is a newly discovered method that can compromise the security of most Virtual Private Network (VPN) applications by diverting traffic away from the encrypted tunnel, exposing it to potential interception.
New Case Study: The Malicious Comment
07 May 2024
How safe is your comments section? Discover how a seemingly innocent 'thank you' comment on a product page concealed a malicious vulnerability, underscoring the necessity of robust security measures. Read the full real-life case study here.
When is a ‘Thank you’ not a ‘Thank you’? When it’s a sneaky bit of code that’s been hidden inside a ‘Thank You’
Google Simplifies 2-Factor Authentication Setup (It's More Important Than Ever)
07 May 2024
Google on Monday announced that it's simplifying the process of enabling two-factor authentication (2FA) for users with personal and Workspace accounts.
Also called, 2-Step Verification (2SV), it aims to add an extra layer of security to users' accounts to prevent takeover attacks in case the passwords are stolen.
The new change entails adding a second step method, such as an
Mastodon Delays Firm Fix to Solve Link Preview DDoS Issue
07 May 2024
Mastodon delayed a firm fix for link preview DDoS issues, pushing it back to version 4.4.0 from the expected 4.3.0 release. The issue arises from the decentralized nature of Mastodon, where link previews generate excessive traffic on host servers.
Russian Operator of BTC-e Crypto Exchange Pleads Guilty to Money Laundering
07 May 2024
A Russian operator of a now-dismantled BTC-e cryptocurrency exchange has pleaded guilty to money laundering charges from 2011 to 2017.
Alexander Vinnik, 44, was charged in January 2017 and taken into custody in Greece in July 2017. He was subsequently extradited to the U.S. in August 2022. Vinnik and his co-conspirators have been accused of owning and managing
WordPress Plugin Exploit Impacts Over 90,000 Websites
07 May 2024
The vulnerability, which has a CVSS score of 9.8, is a SQL injection flaw that allows attackers to execute unauthorized SQL queries and potentially compromise the integrity and confidentiality of the WordPress database.
Cuckoo Mac Malware Mimics Music Converter to Steals Passwords and Crypto
07 May 2024
Cuckoo employs deceptive tactics, claiming to convert Spotify music to MP3 format while actually stealing sensitive data like passwords, browsing history, cryptocurrency wallet details, and more.
Citrix Addresses High-Severity NetScaler Servers Flaw
07 May 2024
Citrix appears to have quietly addressed a vulnerability in its NetScaler ADC and Gateway appliances that gave remote, unauthenticated attackers a way to obtain potentially sensitive information from the memory of affected systems.
NATO and the EU Formally Condemned APT28 Cyber Espionage
07 May 2024
The nation-state actor APT28 exploited the zero-day flaw CVE-2023-23397 in attacks against European entities since April 2022. The Russia-linked APT also targeted NATO entities and Ukrainian government agencies.
Anetac Raises $16M in Funding
07 May 2024
Anetac, a startup protecting companies from blind spots of service accounts in hybrid environments, raised $16M in funding. The round was led by Liberty Global with participation from Shield Capital, GP Ventures, Anetac CEO Tim Eades and Jason Witty.
UK armed forces’ personal data hacked in MoD breach
06 May 2024
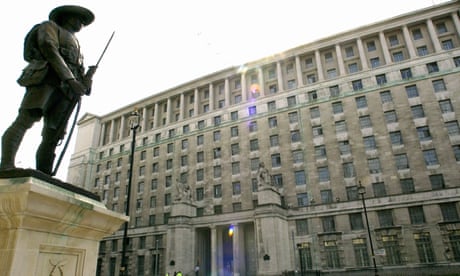 Defence secretary to address MPs after names and bank details of armed forces members targeted by unnamed attackerThe Ministry of Defence has suffered a significant data breach and the personal information of UK military personnel has been hacked.A third-party payroll system used by the MoD, which includes names and bank details of current and past members of the armed forces, was targeted in the attack. A very small number of addresses may also have been accessed. Continue reading...