Latest Cybersecurity News and Articles
Third-Party Cyber Attacks: The Threat No One Sees Coming – Here's How to Stop Them
06 June 2024
Learn about critical threats that can impact your organization and the bad actors behind them from Cybersixgill’s threat experts. Each story shines a light on underground activities, the threat actors involved, and why you should care, along with what you can do to mitigate risk.
In an increasingly interconnected world, supply chain attacks have emerged as a formidable threat, compromising
Prevent Account Takeover with Better Password Security
06 June 2024
Tom works for a reputable financial institution. He has a long, complex password that would be near-impossible to guess. He’s memorized it by heart, so he started using it for his social media accounts and on his personal devices too. Unbeknownst to Tom, one of these sites has had its password database compromised by hackers and put it up for sale on the dark web. Now threat actors are working
Hackers Exploit Legitimate Packer Software to Spread Malware Undetected
06 June 2024
Threat actors are increasingly abusing legitimate and commercially available packer software such as BoxedApp to evade detection and distribute malware such as remote access trojans and information stealers.
"The majority of the attributed malicious samples targeted financial institutions and government industries," Check Point security researcher Jiri Vinopal said in an analysis.
The volume of
Google Maps Timeline Data to be Stored Locally on Your Device for Privacy
06 June 2024
Google has announced plans to store Maps Timeline data locally on users' devices instead of their Google account effective December 1, 2024.
The changes were originally announced by the tech giant in December 2023, alongside changes to the auto-delete control when enabling Location History by setting it to three months by default, down from the previous limit of 18 months.
Google Maps Timeline,
Hackers Target Python Developers with Fake "Crytic-Compilers" Package on PyPI
06 June 2024
Cybersecurity researchers have discovered a malicious Python package uploaded to the Python Package Index (PyPI) repository that's designed to deliver an information stealer called Lumma (aka LummaC2).
The package in question is crytic-compilers, a typosquatted version of a legitimate library named crytic-compile. The rogue package was downloaded 441 times before it was taken down by PyPI
Research reveals top 10 malware detections
05 June 2024
The top 10 malware detections have been revealed in new research.
29% of organizations have added data security to their AI systems
05 June 2024
Artificial intelligence (AI) security and employee preparation was analyzed in a recent survey by SHI International and Dell Technologies.
83% of organizations faced at least one account takeover the past year
05 June 2024
A new survey reveals that account takeovers are a prominent threat.
Chinese State-Backed Cyber Espionage Targets Southeast Asian Government
05 June 2024
An unnamed high-profile government organization in Southeast Asia emerged as the target of a "complex, long-running" Chinese state-sponsored cyber espionage operation codenamed Crimson Palace.
"The overall goal behind the campaign was to maintain access to the target network for cyberespionage in support of Chinese state interests," Sophos researchers Paul Jaramillo, Morgan Demboski, Sean
Who are Qilin, the cybercriminals thought behind the London hospitals hack?
05 June 2024
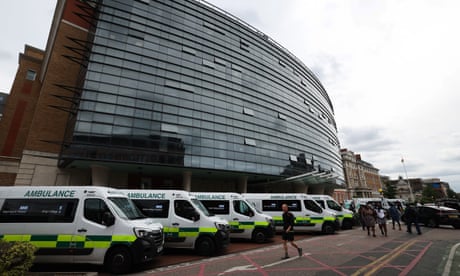 Russian-speaking ransomware gang lets hackers use its tools in exchange for cut of proceedsA Russian-speaking ransomware criminal gang called Qilin is thought to be behind the cyber-attack on NHS medical services provider Synnovis, that halted tests and operations at hospital trusts to a halt and affected GPs across London.Although the location of the group is unknown, if it is based in Russia, it will be difficult for British law enforcement to directly target it. The Russian state has long had a ban on extraditing criminals overseas, and since it launched a full-scale invasion of Ukraine, it has largely ended all cooperation on cybersecurity matters so long as the hackers focus their attacks on foreign targets. Continue reading...
Unpacking 2024's SaaS Threat Predictions
05 June 2024
Early in 2024, Wing Security released its State of SaaS Security report, offering surprising insights into emerging threats and best practices in the SaaS domain. Now, halfway through the year, several SaaS threat predictions from the report have already proven accurate. Fortunately, SaaS Security Posture Management (SSPM) solutions have prioritized mitigation capabilities to address many of
Rebranded Knight Ransomware Targeting Healthcare and Businesses Worldwide
05 June 2024
An analysis of a nascent ransomware strain called RansomHub has revealed it to be an updated and rebranded version of Knight ransomware, itself an evolution of another ransomware known as Cyclops.
Knight (aka Cyclops 2.0) ransomware first arrived in May 2023, employing double extortion tactics to steal and encrypt victims' data for financial gain. It's operational across multiple platforms,
Zyxel Releases Patches for Firmware Vulnerabilities in EoL NAS Models
05 June 2024
Zyxel has released security updates to address critical flaws impacting two of its network-attached storage (NAS) devices that have currently reached end-of-life (EoL) status.
Successful exploitation of three of the five vulnerabilities could permit an unauthenticated attacker to execute operating system (OS) commands and arbitrary code on affected installations.
Impacted models include NAS326
Celebrity TikTok Accounts Compromised Using Zero-Click Attack via DMs
05 June 2024
Popular video-sharing platform TikTok has acknowledged a security issue that has been exploited by threat actors to take control of high-profile accounts on the platform.
The development was first reported by Semafor and Forbes, which detailed a zero-click account takeover campaign that allows malware propagated via direct messages to compromise brand and celebrity accounts without having to
Security leaders respond to Ticketmaster breach
05 June 2024
The ShinyHunters threat operation has claimed to hack Ticketmaster, and security leaders are sharing their thoughts.
Security’s Top 5 – April 2024
05 June 2024
Top stories and new developments from across the security industry throughout April.
Women face nearly twice as much exclusion in cybersecurity than men
04 June 2024
A recent report finds notable gender disparities in the cybersecurity industry.
Russian Power Companies, IT Firms, and Govt Agencies Hit by Decoy Dog Trojan
04 June 2024
Russian organizations are at the receiving end of cyber attacks that have been found to deliver a Windows version of a malware called Decoy Dog.
Cybersecurity company Positive Technologies is tracking the activity cluster under the name Operation Lahat, attributing it to an advanced persistent threat (APT) group called HellHounds.
"The Hellhounds group compromises organizations they select and
Telerik Report Server Flaw Could Let Attackers Create Rogue Admin Accounts
04 June 2024
Progress Software has rolled out updates to address a critical security flaw impacting the Telerik Report Server that could be potentially exploited by a remote attacker to bypass authentication and create rogue administrator users.
The issue, tracked as CVE-2024-4358, carries a CVSS score of 9.8 out of a maximum of 10.0.
"In Progress Telerik Report Server, version 2024 Q1 (10.0.24.305) or
Administrator of 911 S5 botnet arrested, botnet dismantled
04 June 2024
A coordinated international operation had led to the apprehension of the alleged 911 S5 botnet administrator.