Latest Cybersecurity News and Articles
California Privacy Regulator to Partner With French Data Authority
28 June 2024
The California Privacy Protection Agency (CPPA) has signed a partnership agreement with France's Commission Nationale de l'Informatique et des Libertés (CNIL) to conduct joint research and share investigative findings on data privacy issues.
Mitigating Skeleton Key, a New Type of Generative AI Jailbreak Technique
28 June 2024
Microsoft has discovered a new type of jailbreak attack called Skeleton Key. This technique uses a multi-turn strategy to make the model ignore its guardrails, allowing it to generate forbidden content or override its decision-making rules.
Researchers Warn of Flaws in Widely Used Industrial Gas Analysis Equipment
28 June 2024
Multiple security flaws have been disclosed in Emerson Rosemount gas chromatographs that could be exploited by malicious actors to obtain sensitive information, induce a denial-of-service (DoS) condition, and even execute arbitrary commands.
The flaws impact GC370XA, GC700XA, and GC1500XA and reside in versions 4.1.5 and prior.
According to operational technology (OT) security firm Claroty, the
Vanna AI Prompt Injection Vulnerability Enables RCE
28 June 2024
The Vanna AI library has been found to have a vulnerability (CVE-2024-5565) that could allow for remote code execution (RCE) due to a prompt injection issue related to the Plotly script.
No Patches for Hospital Temperature Monitors' Critical Flaws
28 June 2024
Researchers at Nozomi Networks uncovered four vulnerabilities in Sensor Net Connect and three flaws in the Thermoscan IP desktop application, both made by a division of French firm Proges Plus.
TeamViewer Detects Security Breach in Corporate IT Environment
28 June 2024
TeamViewer on Thursday disclosed it detected an "irregularity" in its internal corporate IT environment on June 26, 2024.
"We immediately activated our response team and procedures, started investigations together with a team of globally renowned cyber security experts and implemented necessary remediation measures," the company said in a statement.
It further noted that its corporate IT
WA man set up fake free wifi at Australian airports and on flights to steal people’s data, police allege
27 June 2024
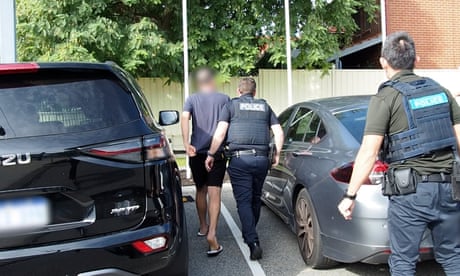 Investigation launched after airline reported a suspicious network popped up during a domestic flight in AprilFollow our Australia news live blog for latest updatesGet our morning and afternoon news emails, free app or daily news podcastA man has been charged after he allegedly set up fake free wifi networks at Australian airports and on domestic flights to steal personal data from unsuspecting members of the public.The 42-year-old Western Australian man is facing nine cybercrime charges and was due to appear in Perth magistrates court on Friday.Sign up for Guardian Australia’s free morning and afternoon email newsletters for your daily news roundup Continue reading...
Rust-Based P2PInfect Botnet Evolves with Miner and Ransomware Payloads
27 June 2024
The peer-to-peer malware botnet known as P2PInfect has been found targeting misconfigured Redis servers with ransomware and cryptocurrency miners.
The development marks the threat's transition from what appeared to be a dormant botnet with unclear motives to a financially motivated operation.
"With its latest updates to the crypto miner, ransomware payload, and rootkit elements, it demonstrates
PoC Exploit for Critical Fortra FileCatalyst Flaw Published
27 June 2024
The vulnerability allows attackers to create administrative user accounts, modify and delete data in the application database, and potentially gain full control of vulnerable systems.
Malicious NPM Package Targets AWS Users to Deploy Backdoor
27 June 2024
ReversingLabs researchers discovered a suspicious package on npm called legacyreact-aws-s3-typescript. They found that the package contained a post-install script that downloaded and executed a simple backdoor.
Korean Telco Allegedly Infected Around 600,000 P2P Users with Malware
27 June 2024
South Korean telco KT has been accused of purposely infecting customers with malware as a result of excessive use of peer-to-peer (P2P) downloading tools. Around 600,000 users of online storage services have reportedly been affected.
The Secrets of Hidden AI Training on Your Data
27 June 2024
While some SaaS threats are clear and visible, others are hidden in plain sight, both posing significant risks to your organization. Wing's research indicates that an astounding 99.7% of organizations utilize applications embedded with AI functionalities. These AI-driven tools are indispensable, providing seamless experiences from collaboration and communication to work management and
Novel Snowblind Malware Targets Banking Customers in Southeast Asia
27 June 2024
Snowblind is effective on all modern Android devices and primarily targets banking apps. It avoids detection by modifying the app and exploiting the Linux kernel's seccomp feature to control the app's system calls.
How to Use Python to Build Secure Blockchain Applications
27 June 2024
Did you know it’s now possible to build blockchain applications, known also as decentralized applications (or “dApps” for short) in native Python? Blockchain development has traditionally required learning specialized languages, creating a barrier for many developers… until now. AlgoKit, an all-in-one development toolkit for Algorand, enables developers to build blockchain applications in pure
Phantom Secrets: Undetected Secrets Expose Major Corporations
27 June 2024
Major secrets, including cloud environment credentials, internal infrastructures, and telemetry platforms, have been found exposed on the internet due to Git-based processes and Source Code Management (SCM) platforms behavior.
Prompt Injection Flaw in Vanna AI Exposes Databases to RCE Attacks
27 June 2024
Cybersecurity researchers have disclosed a high-severity security flaw in the Vanna.AI library that could be exploited to achieve remote code execution vulnerability via prompt injection techniques.
The vulnerability, tracked as CVE-2024-5565 (CVSS score: 8.1), relates to a case of prompt injection in the "ask" function that could be exploited to trick the library into executing arbitrary
Update: MOVEit Transfer Vulnerability Targeted Amid Disclosure Drama
27 June 2024
The non-profit cybersecurity organization, the Shadowserver Foundation, has observed exploitation attempts against CVE-2024-5806. They noted that the exploitation began soon after the vulnerability details were made public.
Chinese Cyberspies Employ Ransomware in Attacks for Diversion
27 June 2024
The adoption of ransomware in cyberespionage attacks helps adversaries blur the lines between APT and cybercriminal activity, leading to potential misattribution or concealing the true nature of the operation.
Russian National Indicted for Cyber Attacks on Ukraine Before 2022 Invasion
27 June 2024
A 22-year-old Russian national has been indicted in the U.S. for his alleged role in staging destructive cyber attacks against Ukraine and its allies in the days leading to Russia's full-blown military invasion of Ukraine in early 2022.
Amin Timovich Stigal, the defendant in question, is assessed to be affiliated with the Main Directorate of the General Staff of the Armed Forces of the Russian
Critical ADOdb Vulnerabilities Fixed in Ubuntu
27 June 2024
These vulnerabilities include SQL injection attacks, cross-site scripting (XSS) attacks, and authentication bypasses. Ubuntu has released updates for various versions, including Ubuntu 22.04 LTS, 20.04 LTS, 18.04 ESM, and 16.04 ESM.